
RansomHub
From extortion.wiki, the ransomware negotiation research archive
Negotiation records classified under RansomHub in the current Ransomchats snapshot. This page indexes the source label; it does not independently verify attribution.
Classification follows the source dataset. Metadata is useful. It is not testimony.
Actor lineage
Global lineage directoryOverview
Government and MITRE reporting link RansomHub resources to Knight/Cyclops, while MITRE explicitly frames operator continuity as possible rather than established. This record therefore uses a code-overlap relationship, not a confirmed rebrand.
Documentary media
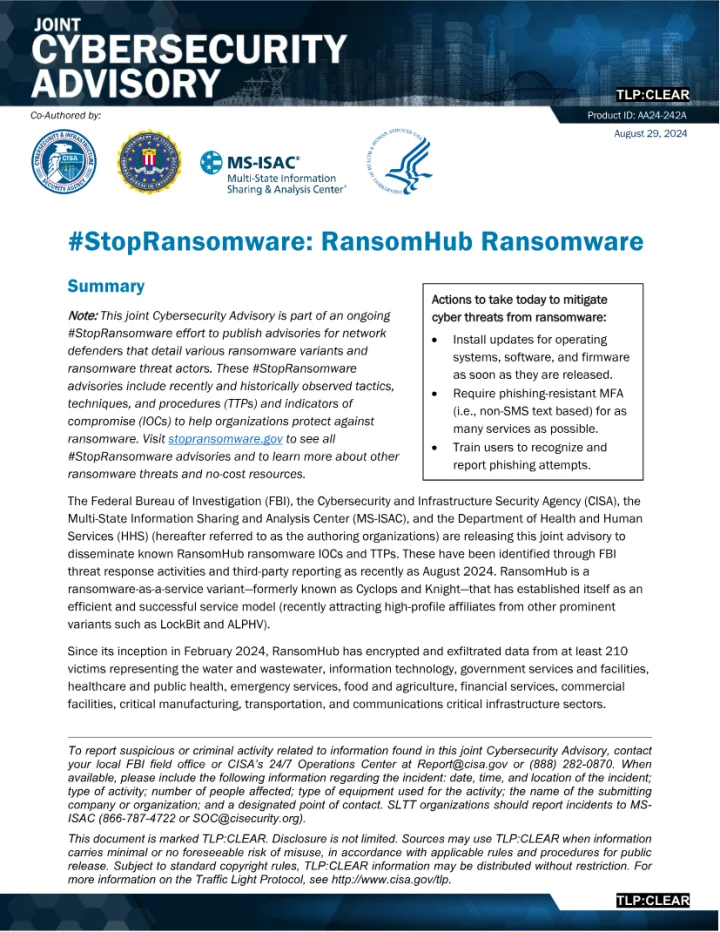
Known aliases
No source-supported alias is currently recorded. Malware names and actor-group names are not assumed to be equivalent.
Historical timeline
-
RansomHub first observed
RansomHub activity begins
The joint advisory describes RansomHub as active since February 2024.
Evidence status: officially confirmed ConfirmedRelated: Knight ransomware
Lineage and relationships
| Related actor or family | Relationship | Period | Confidence | Evidence summary | Sources |
|---|---|---|---|---|---|
| Knight ransomwareransomware family | Code overlapsuspected · directed | From February 2024 | Moderate confidence | MITRE reports that RansomHub operators may have purchased and rebranded Knight resources and notes code, feature, and infrastructure overlaps. The same source does not establish that Knight's operators became RansomHub.
| FBI, CISA, MS-ISAC, and HHS · MITRE ATT&CK |
Predecessors
None established.
Successors
None established.
Splits and mergers
None established.
Suspected affiliate relationships
None established.
MITRE ATT&CK integration
No explicit MITRE ATT&CK group mapping is published for this source label. Software entries and fuzzy name matches are not promoted to group mappings.
External intelligence references
- #StopRansomware: RansomHub RansomwareFBI, CISA, MS-ISAC, and HHS · government advisory · primary authoritative
- RansomHub, Software S1212MITRE ATT&CK · MITRE ATTACK · authoritative secondary
Confidence and evidence notes
Confidence applies to each individual alias, event, or relationship—not to the actor page as a whole. “Confirmed” requires explicit authoritative attribution or multiple strong independent sources. Moderate, low, disputed, and unknown entries retain the source's uncertainty. A malware-family name is not automatically an actor identity, and shared code or affiliates do not prove shared leadership.
Ransomware notes
Browse Ransomhub notesThe explicit archive alias mapping connects this Ransomchats actor label to the ThreatLabz family Ransomhub. Its 4 archived notes are counted and searched separately from the negotiation records below.
Search within this collection
Negotiation records
No matching records
No records match the current filters. Remove one before blaming the archive.