
Actor lineage & alias timeline
From extortion.wiki, the ransomware documentary archive
A source-linked directory of historical names, rebrands, succession claims, code lineage, affiliate overlap, and infrastructure disruptions. Every published claim retains its relationship type, confidence, evidence summary, and sources.
Shared malware, language, infrastructure style, negotiation behavior, or affiliates do not establish common operators. Empty sections are deliberate: the archive does not fill evidence gaps with inference.
Documented timeline
25 source-linked eventsMajor observations, enforcement actions, disruptions, and qualified lineage reports. Documentary thumbnails are local archival derivatives; the universal neutral silhouette is labeled and never presented as historical evidence.
-
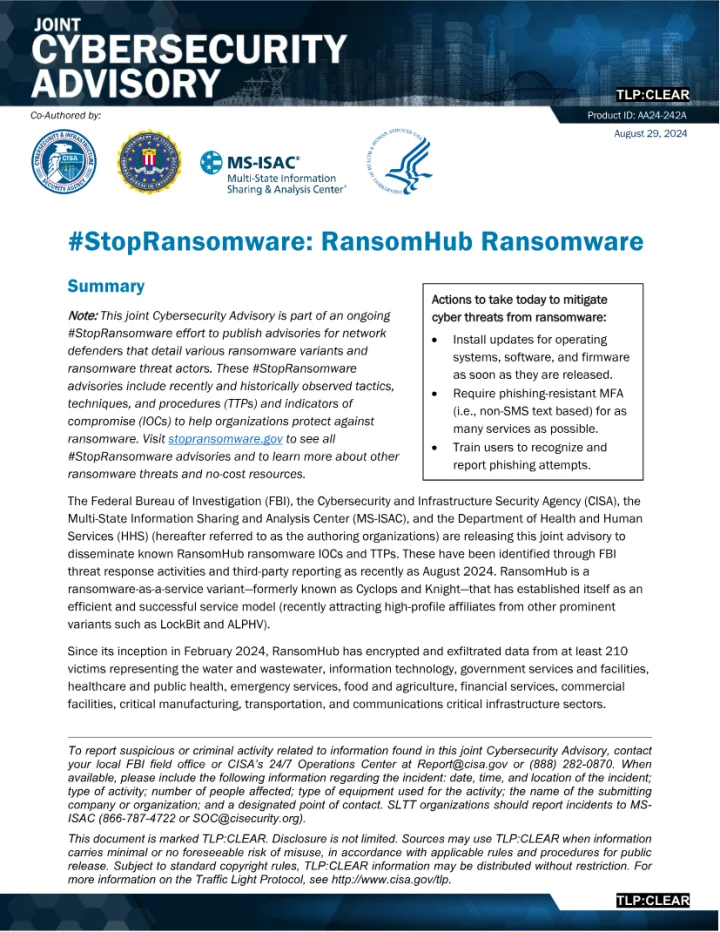
Knight ransomware disputed event
Knight resources linked to RansomHub reporting
The joint RansomHub advisory and MITRE reporting connect RansomHub resources to Knight/Cyclops. MITRE frames purchase and rebranding as possible, so this event documents code or resource lineage rather than confirmed operator continuity.
Evidence status: officially confirmed Moderate confidenceRelated: RansomHub
-
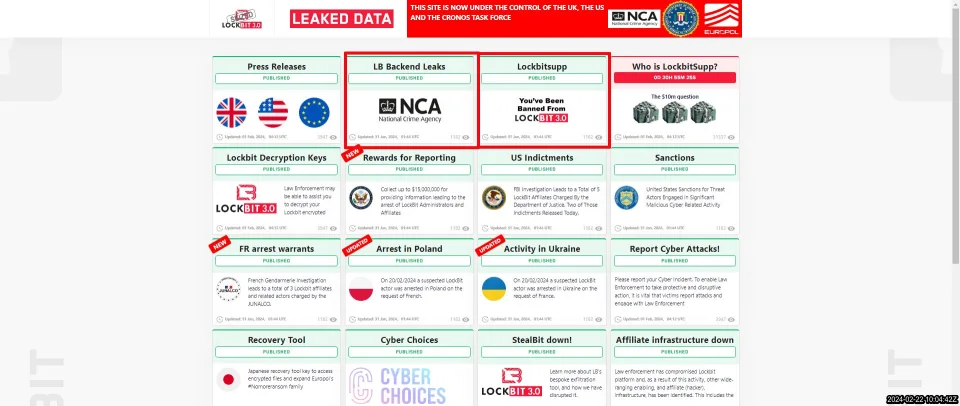
LockBit infrastructure disrupted
Operation Cronos disrupts LockBit infrastructure
The NCA announced an international operation that infiltrated LockBit's network and took control of services, including its leak site. The event is a disruption, not a claim that all later activity ceased.
Evidence status: officially confirmed Confirmed -
RansomHub first observed
RansomHub activity begins
The joint advisory describes RansomHub as active since February 2024.
Evidence status: officially confirmed ConfirmedRelated: Knight ransomware
-
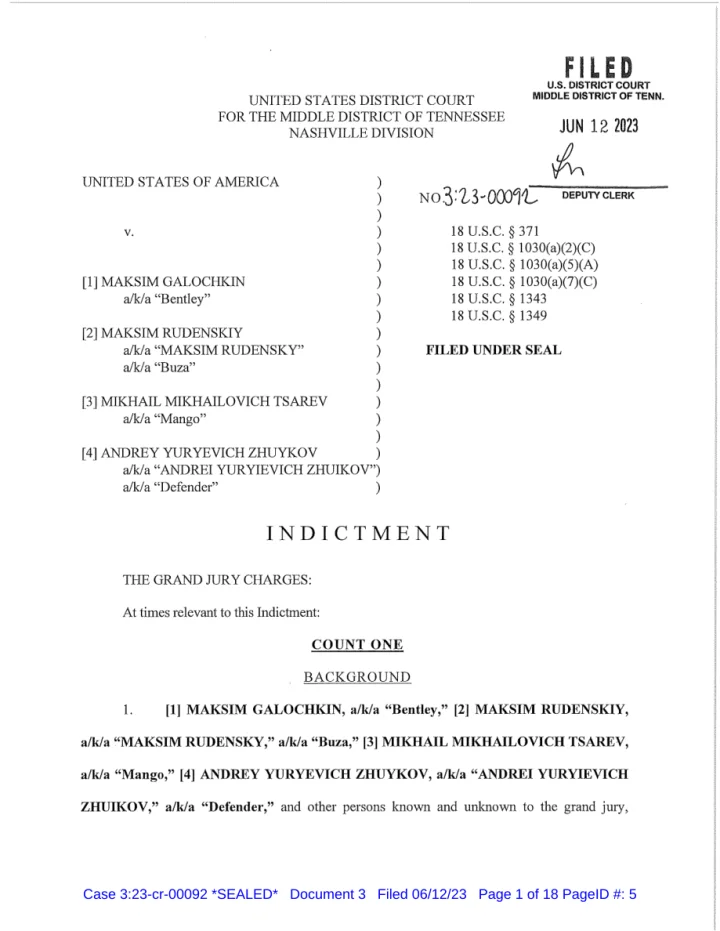
Conti indictment
Conti-related indictments unsealed
DOJ announced that three indictments had been unsealed and charged multiple foreign nationals in Conti ransomware and Trickbot malware conspiracies. The charges are allegations; the defendants are presumed innocent unless proven guilty.
Evidence status: officially confirmed Confirmed -
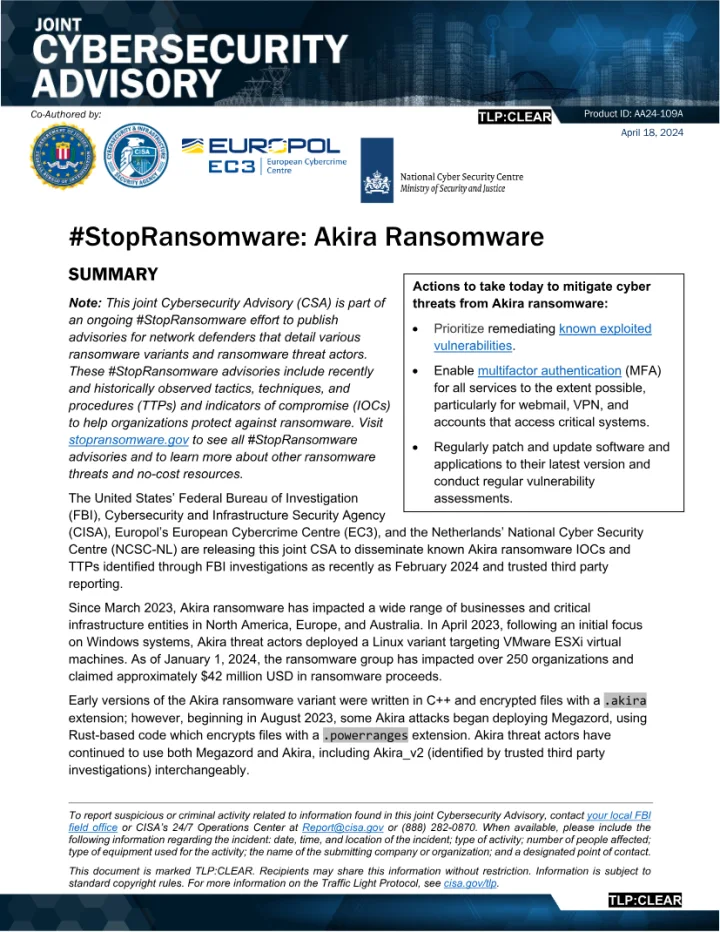
Akira first observed
Akira activity observed
The joint advisory documents Akira ransomware activity from March 2023.
Evidence status: officially confirmed Confirmed -
No verified documentary image available. Hive leak site seized
Hive servers and websites seized
DOJ announced that U.S., German, and Dutch authorities seized control of Hive servers and websites, disrupting its ability to attack and extort victims.
Evidence status: official disruption record ConfirmedSeizure banners: Hive
-
LockBit alias observed
LockBit Green appears
The joint advisory reports that LockBit Green incorporated Conti ransomware source code; this is code lineage, not proof of shared operators.
Evidence status: officially confirmed High confidenceRelated: Conti
-
Qilin rebrand
Agenda rebrands as Qilin
HHS HC3 reports that the operation had rebranded from Agenda to Qilin by September 2022.
Evidence status: officially confirmed Confirmed -
Qilin operation launched
Operation launches as Agenda
HHS HC3 reports that the operation initially launched as Agenda in July 2022.
Evidence status: officially confirmed Confirmed -
No verified documentary image available. Hive infrastructure disrupted
FBI infiltration begins
DOJ says the FBI penetrated Hive's networks in late July 2022 and began providing decryption keys to victims.
Evidence status: official disruption record Confirmed -
Black Basta first observed
Black Basta first identified
The joint advisory states that the Black Basta RaaS variant was first identified in April 2022.
Evidence status: officially confirmed Confirmed -
LockBit alias observed
LockBit 3.0 / LockBit Black emerges
The joint advisory records the emergence of LockBit 3.0, also known as LockBit Black.
Evidence status: officially confirmed Confirmed -
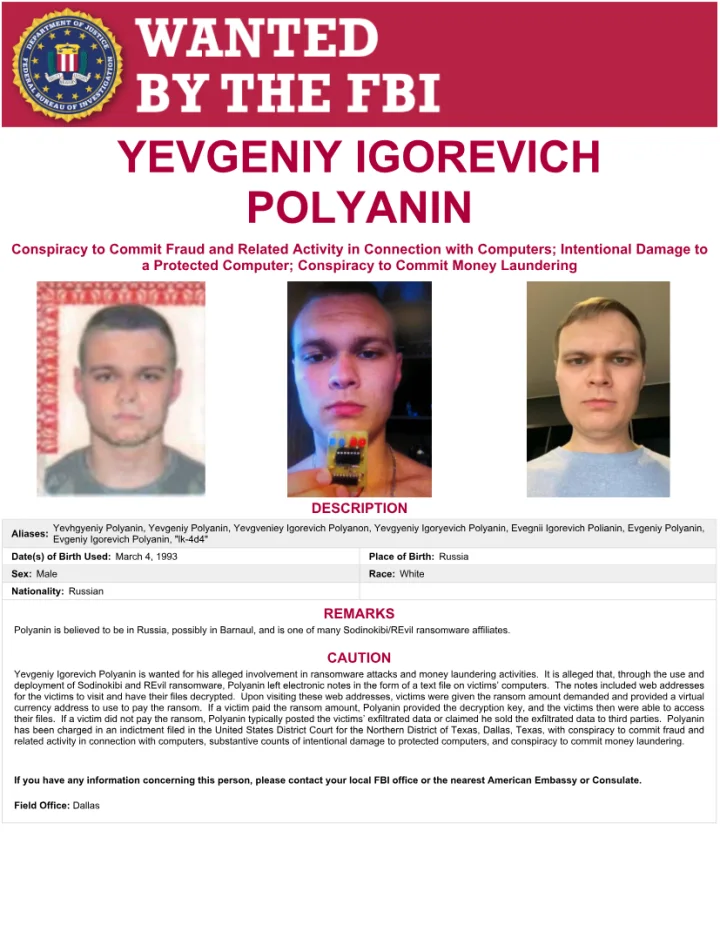
REvil indictment
DOJ announces charges, arrest, and seizure
DOJ announced charges against two alleged Sodinokibi/REvil actors, an arrest, and seizure of funds traceable to alleged ransom payments.
Evidence status: officially confirmed Confirmed -
BlackMatter first observed
BlackMatter first observed
The joint advisory records BlackMatter as first seen in July 2021.
Evidence status: officially confirmed ConfirmedRelated: DarkSide
-
BlackMatter disputed event
Possible DarkSide rebrand reported
CISA, FBI, and NSA describe BlackMatter as a possible DarkSide rebrand; the advisory does not confirm full operator continuity.
Evidence status: officially confirmed Moderate confidenceRelated: DarkSide
-
DarkSide asset seizure
DOJ announces seizure of ransom proceeds
DOJ announced the seizure of 63.7 bitcoin then valued at approximately USD 2.3 million and alleged to represent proceeds from the Colonial Pipeline ransom payment to DarkSide. The seizure does not identify every DarkSide operator.
Evidence status: officially confirmed Confirmed -
No verified documentary image available. Hive first observed
Hive activity documented
DOJ reports that Hive targeted victims from June 2021.
Evidence status: source-supported observation Confirmed -
AvosLocker first observed
AvosLocker first observed
MITRE records AvosLocker as first observed in June 2021.
Evidence status: officially confirmed High confidence -
LockBit alias observed
LockBit 2.0 / LockBit Red appears
The joint advisory records the appearance of LockBit 2.0, also known as LockBit Red.
Evidence status: officially confirmed Confirmed -
DarkSide last observed
End of reported DarkSide activity period
The same advisory bounds the reported DarkSide RaaS activity period through May 2021.
Evidence status: officially confirmed High confidenceRelated: BlackMatter
-
DarkSide first observed
DarkSide activity begins
The joint BlackMatter advisory describes DarkSide RaaS as active from September 2020.
Evidence status: officially confirmed High confidence -
LockBit operation launched
LockBit name appears
LockBit-named ransomware appeared on Russian-language cybercrime forums in January 2020.
Evidence status: officially confirmed ConfirmedRelated: ABCD ransomware
-
No verified documentary image available. Conti first observed
Conti ransomware first observed
MITRE records the Conti RaaS as first observed in December 2019.
Evidence status: source-supported observation High confidence -
ABCD ransomware first observed
ABCD ransomware activity observed
The joint advisory dates first observed ABCD ransomware activity to September 2019 and identifies it as LockBit's predecessor.
Evidence status: officially confirmed ConfirmedRelated: LockBit
-
No verified documentary image available. REvil first observed
REvil/Sodinokibi first observed
MITRE records the REvil ransomware family and RaaS as operating since at least April 2019.
Evidence status: source-supported observation High confidence
Alphabetical actor index
26 archive actors · 13 curated evidence entities| Source actor | Canonical lineage | Aliases | Relationships | Negotiations | Ransomware notes | Evidence status |
|---|---|---|---|---|---|---|
| ABCD ransomwareEvidence-only entity | ABCD ransomware | 0 | 1 | — | — | Sources attached |
| Akira | Akira | 0 | 0 | 60 | 3 | Sources attached |
| Avaddon | Not curated | 0 | 0 | 7 | 1 | No lineage claims published |
| Avos | AvosLocker | 1 | 0 | 1 | 1 | Sources attached |
| Babuk | Not curated | 0 | 0 | 2 | 0 | No lineage claims published |
| BlackBasta | Black Basta | 0 | 1 | 5 | 5 | Sources attached |
| BlackMatter | BlackMatter | 0 | 1 | 2 | 1 | Sources attached |
| Cloak | Not curated | 0 | 0 | 2 | 3 | No lineage claims published |
| Conti | Conti | 0 | 2 | 32 | 4 | Sources attached |
| Darkside | DarkSide | 0 | 1 | 5 | 1 | Sources attached |
| Dragonforce | Not curated | 0 | 0 | 14 | 2 | No lineage claims published |
| fog | Not curated | 0 | 0 | 6 | 2 | No lineage claims published |
| Hive | Hive | 0 | 0 | 8 | 2 | Sources attached |
| Hunters International | Not curated | 0 | 0 | 1 | 3 | No lineage claims published |
| kairos | Not curated | 0 | 0 | 1 | 1 | No lineage claims published |
| Knight ransomwareEvidence-only entity | Knight ransomware | 1 | 1 | — | — | Sources attached |
| lockbit3.0 | LockBit | 5 | 2 | 42 | 5 | Sources attached |
| Mallox | Not curated | 0 | 0 | 3 | 2 | No lineage claims published |
| mount-locker | Not curated | 0 | 0 | 1 | 0 | No lineage claims published |
| Nightspire | Not curated | 0 | 0 | 7 | 4 | No lineage claims published |
| NoEscape | Not curated | 0 | 0 | 2 | 3 | No lineage claims published |
| Pear | Not curated | 0 | 0 | 1 | 0 | No lineage claims published |
| Qilin | Qilin | 1 | 0 | 2 | 3 | Sources attached |
| RansomHub | RansomHub | 0 | 1 | 1 | 4 | Sources attached |
| Ranzy | Not curated | 0 | 0 | 2 | 1 | No lineage claims published |
| REvil | REvil | 2 | 0 | 20 | 3 | Sources attached |
| RunSomeWares | Not curated | 0 | 0 | 1 | 0 | No lineage claims published |
| trinity | Not curated | 0 | 0 | 14 | 1 | No lineage claims published |
Actors with known predecessors or successors
- ABCD ransomware → LockBit Predecessor · Confirmed
The joint LockBit advisory explicitly calls ABCD ransomware the predecessor to LockBit. This describes ransomware lineage and does not by itself prove uninterrupted operator identity.
CISA, FBI, MS-ISAC, and international partners
Known and reported rebrands
- Cyclops → Knight ransomware Former name · High confidence
Government and MITRE reporting identify Knight as formerly Cyclops; exact dates are not established in this snapshot.
FBI, CISA, MS-ISAC, and HHS · MITRE ATT&CK - Agenda → Qilin Former name · Confirmed
HHS HC3 reports that the operation launched as Agenda in July 2022 and had rebranded as Qilin by September 2022.
MITRE ATT&CK · U.S. Department of Health and Human Services, Health Sector Cybersecurity Coordination Center - DarkSide → BlackMatter Rebrand · Moderate confidence
CISA, FBI, and NSA describe BlackMatter as a possible DarkSide rebrand. The source does not confirm complete operator continuity.
CISA, FBI, and NSA
Known splits
No split relationship currently meets the evidence threshold.
Known mergers
No merger relationship currently meets the evidence threshold.
Disputed relationships
No relationship in this snapshot is marked disputed. Suspected and moderate-confidence records remain visibly separate from confirmed records.
Recently updated lineage records
Relationship directory
| Source | Relationship | Target | Period | Confidence | Evidence summary | Sources |
|---|---|---|---|---|---|---|
| Conti | Code overlapsupported · undirected | LockBit | From January 2023 | High confidence | The joint LockBit advisory reports that LockBit Green incorporated Conti ransomware source code. Code reuse is not evidence that the operations shared leadership.
| CISA, FBI, MS-ISAC, and international partners |
| Knight ransomware | Code overlapsuspected · directed | RansomHub | From February 2024 | Moderate confidence | MITRE reports that RansomHub operators may have purchased and rebranded Knight resources and notes code, feature, and infrastructure overlaps. The same source does not establish that Knight's operators became RansomHub.
| FBI, CISA, MS-ISAC, and HHS · MITRE ATT&CK |
| ABCD ransomware | Predecessorconfirmed · directed | LockBit | From September 2019 | Confirmed | The joint LockBit advisory explicitly calls ABCD ransomware the predecessor to LockBit. This describes ransomware lineage and does not by itself prove uninterrupted operator identity.
| CISA, FBI, MS-ISAC, and international partners |
| DarkSide | Rebrandsuspected · directed | BlackMatter | From July 2021 | Moderate confidence | CISA, FBI, and NSA describe BlackMatter as a possible DarkSide rebrand. The source does not confirm complete operator continuity.
| CISA, FBI, and NSA |
| Conti | Shared operatorssuspected · undirected | Black Basta | From April 2022 | Moderate confidence | MITRE records researchers' assessment that Black Basta operators could include current or former Conti members. “Could include” is not treated as confirmed membership or succession.
| MITRE ATT&CK |
No matching relationships
No evidence record matches both filters.
Confidence model
- Confirmed
- Explicit authoritative attribution or multiple strong independent sources.
- High confidence
- Strong technical or operational evidence with broad agreement, short of full confirmation.
- Moderate confidence
- Credible reporting or partial technical evidence supports the relationship.
- Low confidence
- Limited, indirect, or preliminary evidence.
- Disputed
- Credible sources disagree.
- Unknown
- Evidence is currently insufficient.
See lineage source attribution for source tiers, MITRE separation, and media-review boundaries.